Challenges
- Interoperability across disparate systems
- Data privacy and security requirements
- Legacy infrastructure supporting live operations
Our approach
- Secure-by-design architecture
- Careful, staged migrations
- Integration-first engineering
Capabilities
What we build for healthcare.
What we design for
The constraints that shape architecture decisions in this sector.
- Access control and audit trails over patient data from the first design
- Encryption in transit and at rest as an architectural default
- Interoperability with the clinical systems already in place
- Defined degradation — clinical workflows cannot stop when an integration fails
Typical engagements
The work teams in this sector most often bring to us.
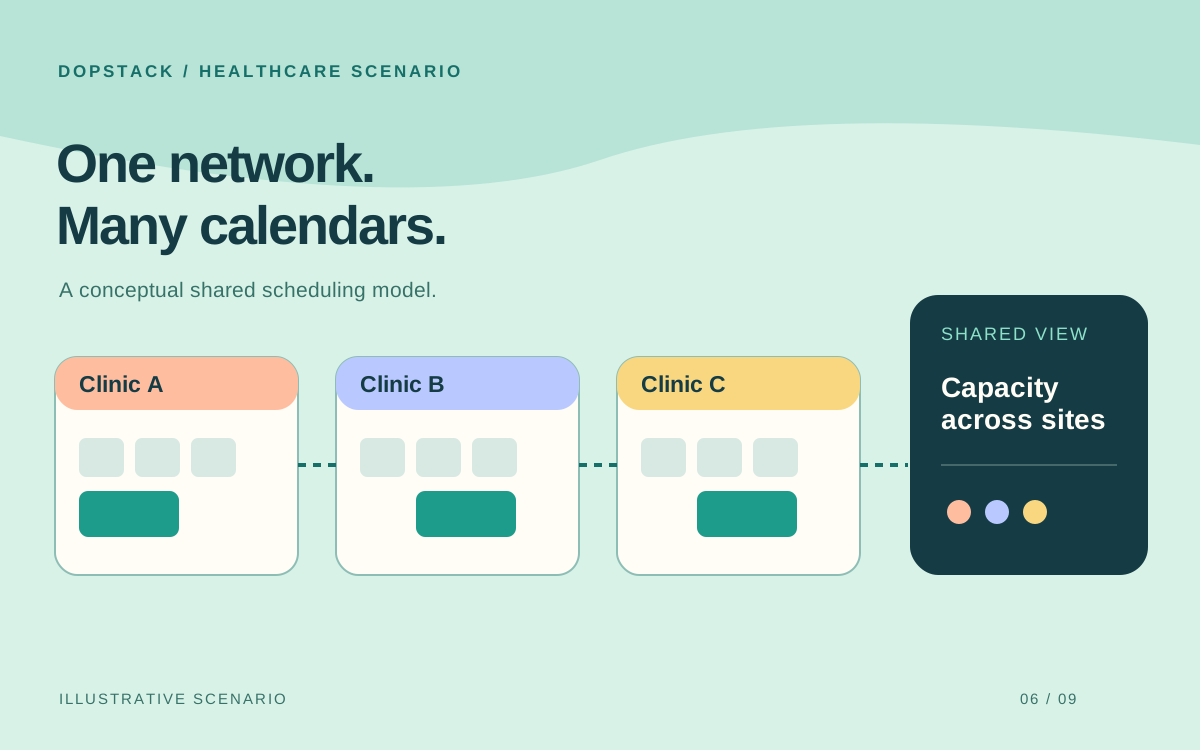
- Unifying scheduling or intake across multiple sites
- Building a patient-facing portal on top of an existing EHR
- Automating document-heavy clinical administration
- Adding analytics across clinical and operational data
Why Dopstack
Why teams in this sector work with us.
From the blog
Related engineering scenarios.
Representative problems and approaches, not published client projects.
Services
How we usually engage here.
FAQ
Questions we get asked.
Is what you build HIPAA compliant?
We design to the controls HIPAA implies — least privilege, encryption, audit logging, access review — and build to the requirements your compliance officer sets. Compliance is a property of your organisation and its processes; no vendor can certify it on your behalf.
Do you replace our EHR?
No. We integrate around it. Anything that asks a clinical site to abandon a system it depends on tends to fail at rollout.
Can you work with our existing integration engine?
Usually. We prefer building adapters behind a single internal interface over introducing a second competing integration layer.