Challenges
- Legacy core systems that resist change
- Strict compliance and audit requirements
- High expectations for uptime and data integrity
Our approach
- Architecture reviews aligned to regulatory requirements
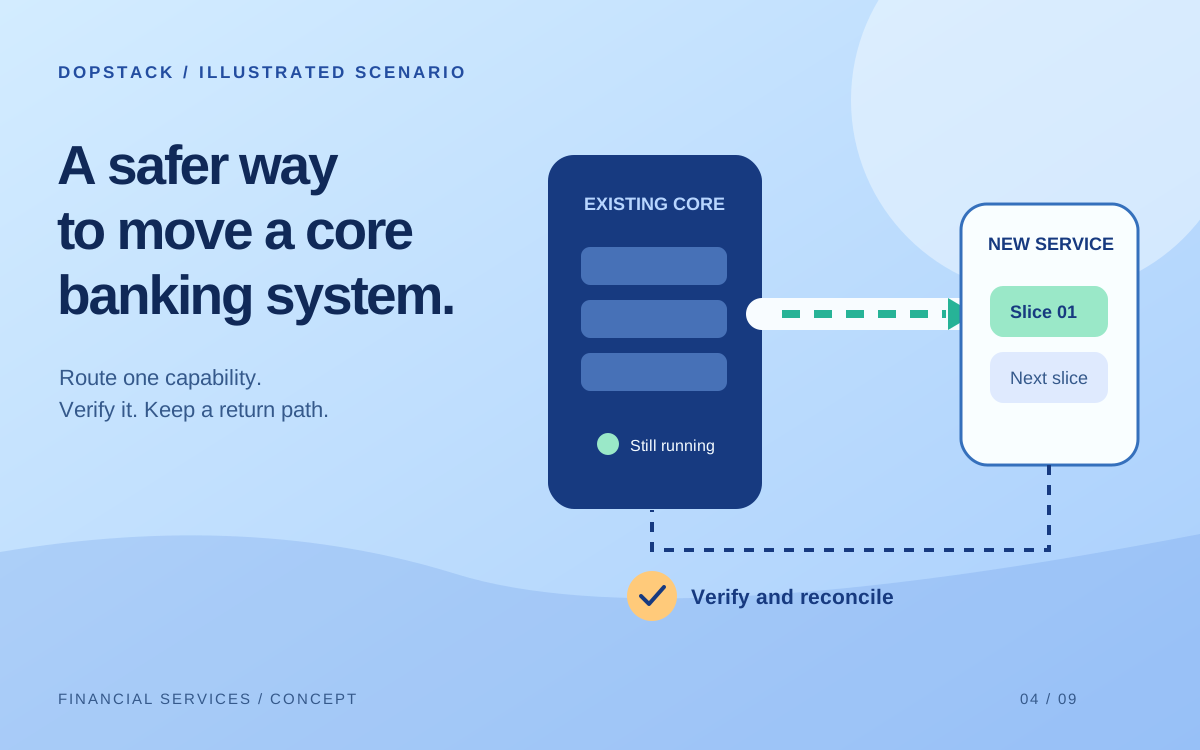
- Incremental modernization without downtime
- Observability built for audit trails
Capabilities
What we build for financial services.
What we design for
The constraints that shape architecture decisions in this sector.
- Auditability: every state change traceable to an actor and a time
- Access control and data residency designed before the first feature
- Reversible releases — money movement cannot absorb a bad deploy
- Reconciliation treated as a system requirement, not a report
Typical engagements
The work teams in this sector most often bring to us.
- Extracting a service out of a core banking monolith
- Building an underwriting or credit-decision workflow
- Integrating open banking or payment provider APIs
- Standing up fraud and risk dashboards over live data
Why Dopstack
Why teams in this sector work with us.
From the blog
Related engineering scenarios.
Representative problems and approaches, not published client projects.
Services
How we usually engage here.
FAQ
Questions we get asked.
Do you handle regulatory compliance for us?
We build systems to meet the requirements your compliance and legal teams define — auditability, access control, data residency, retention. We do not act as a compliance authority or certify a product as compliant; that judgement stays with the people accountable to your regulator.
Can you work alongside our existing core banking vendor?
Yes. Most of our financial services work is integration and extraction around systems that have to keep running, rather than replacing them.
How do you work within our downtime constraints?
By designing for staged rollout — parallel paths, gradual traffic shifting and a rollback at each step — so changes do not depend on a maintenance window.